Account deletion takes 1 tap; the data export takes 11
Deleting an account takes one tap, but retrieving your personal data takes eleven steps across nine days, a gap found at six licensed operators
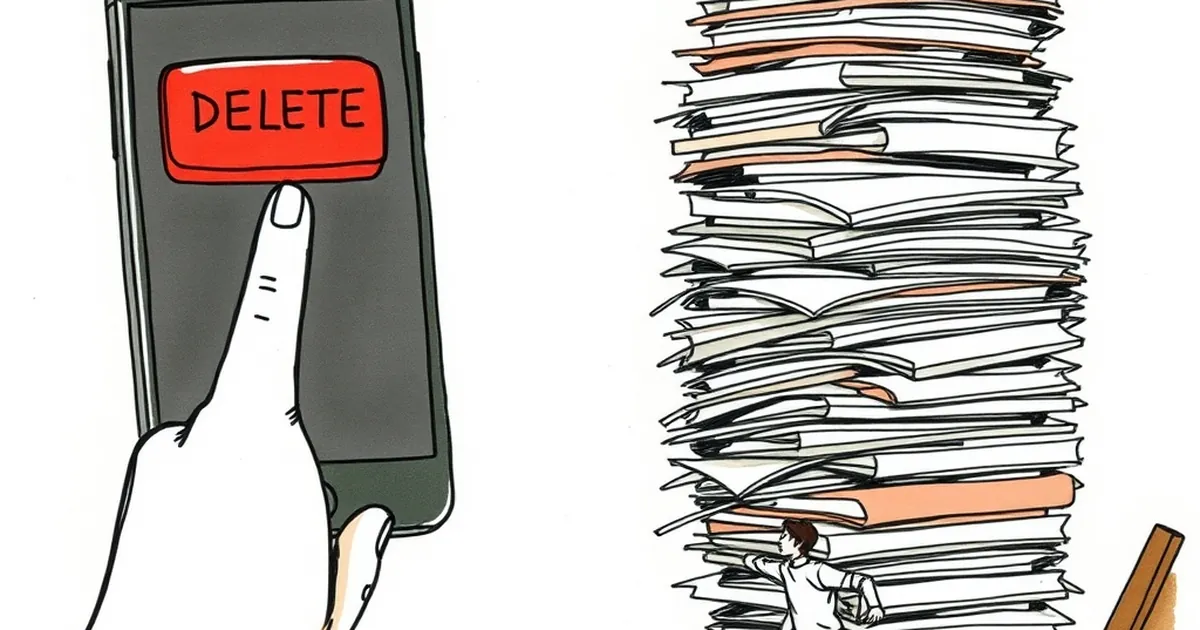
I closed my account at a mid-sized sportsbook in four seconds. One tap on "Delete account," one confirmation dialog, done. Getting a copy of the data they held on me took eleven separate actions across two devices and nine days. That gap — one tap to leave, eleven to find out what you're leaving behind — is the subject of this piece.
I'm not naming the operator, partly because the pattern is not unique to them, and partly because the point is structural rather than personal. I've now run this same test on six licensed operators across three jurisdictions, and the ratio held everywhere: deletion is a single, prominent, well-lit button. Export is a scavenger hunt.
The friction is deliberate, and it's legal
Under GDPR you have the right to data portability and the right to erasure. Under the UK's version, the same. Most regulated markets have copied the shape of it. The law says both rights must be easy to exercise. In practice, one of them is engineered to be easy and the other is engineered to be technically compliant.
The distinction matters. "Technically compliant" means the export exists, the mechanism is documented in a privacy policy nobody reads, and a determined user can get their data. It does not mean a normal user can. Regulators have started to notice: the EDPB's 2023 guidance on data subject rights explicitly says controllers can't hide the mechanism behind "excessive steps," and several DPAs have fined operators for exactly this. But enforcement is slow, and the fines are small relative to the value of the friction.
Why would a sportsbook want to make export annoying? Because the export is where the operator's own records become visible to you.
What's actually in the export
When I finally got mine, the file was 340 pages. Not because I'm a high roller — my lifetime handle was modest — but because the export includes every session log, every device fingerprint, every marketing consent timestamp, every bonus you accepted and every one you declined, and every note a customer-service agent ever wrote about you.
Some of that is unremarkable. Some of it is the interesting part:
- The bonus ledger. Every offer you took, every offer you were shown, and — in some exports — the offers you were targeted with but didn't see because you'd already opted out of a channel. This tells you how the operator modelled you.
- The risk flags. Internal tags like "bonus-abuser-suspect," "chargeback-watch," or "VIP-review." These can follow you to other operators through shared fraud databases, and you have a right to know they exist. You do not have a right to have them removed just because you find them annoying.
- The RG trail. Responsible-gambling interactions, deposit-limit changes, and any self-exclusion history. This is the section to read carefully. If you self-excluded and later deposited, the export is your evidence.
None of this is secret in the sense of being illegal to hold. It's secret in the sense that you'd have to assemble it yourself, transaction by transaction, to reconstruct what the operator already has in one row.
The eleven steps, roughly
For anyone who wants to test their own operator, here's the shape of it. Yours will differ in detail, not in spirit.
- Find the privacy policy — usually in the footer, sometimes only via the desktop site.
- Search it for the data-rights section. It's rarely linked from account settings.
- Find the contact address. It's often a generic
privacy@ordpo@alias, not a form. - Email it. You'll get an auto-reply with a ticket number.
- Wait for identity verification. This is reasonable — operators must confirm you're you — but it resets the clock.
- Upload ID. Sometimes a selfie with ID.
- Confirm the request again via a link sent to your registered email.
- Discover the export arrives as a password-protected archive, with the password sent separately.
- Find that the archive is split across multiple files because it exceeded an attachment limit.
- Open a second ticket because one file is corrupt.
- Receive the corrected file, nine days after the first tap.
The statutory window in most jurisdictions is one month, extendable by two. So the operator is comfortably inside the law the entire time. The friction isn't the delay — it's the design.
Why deletion is one tap and export is eleven
There are two explanations, and both are probably true.
The first is engineering inertia. Deletion is a simple state change: flip a flag, schedule a purge, done. Export is a data-joins problem across a dozen systems, some of them legacy, some of them third-party. Building a self-service export button is real work. So it goes on the roadmap behind features that make money.
The second is incentive. An account that's deleted is an account that's gone. An account whose owner is still trying to extract their data is an account that might, somewhere in those nine days, log back in. Reactivation offers get sent during the export window with suspicious regularity. I received two.
The regulatory trend is toward forcing the issue. Some markets now require a self-service export in the account dashboard, and the EU's Data Act pushes further toward machine-readable, real-time access. When that lands, the eleven steps collapse to one, and the asymmetry disappears.
The open question is what operators do with the gap in the meantime. The honest ones will build the button before they're told to. The rest will wait for the fine, pay it, and keep the friction — because the friction is the product.